• About Us
  • Advertise
AltcoinReporter
  • Home
  • News
    • Bitcoin
    • Ethereum
    • Blockchain
    • Altcoins
    • DeFi
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us
No Result
View All Result
  • Home
  • News
    • Bitcoin
    • Ethereum
    • Blockchain
    • Altcoins
    • DeFi
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us
No Result
View All Result
AltcoinReporter
No Result
View All Result
Home Blockchain

Chainstack Breach Began With a Default Grafana Login and an Open MCP Server

Salar Salek by Salar Salek
November 12, 2026
in Blockchain
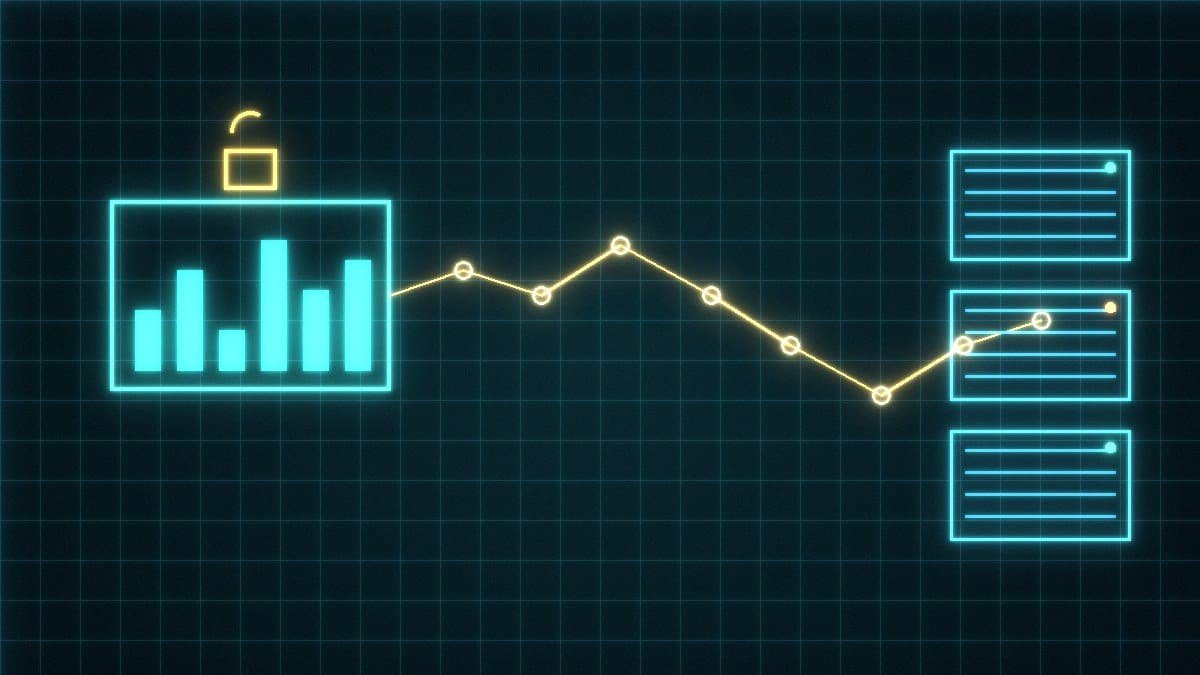
Illustration of an unlocked dashboard panel on a dark grid with a glowing path of linked nodes leading from it to a row of server racks, in teal and amber

Chainstack, the blockchain node and RPC provider, says the attacker who reached its customer database got in through a test Grafana dashboard that was open to the internet with its default administrator password unchanged. From there the intruder found an internal AI tool server that required no login and ran with full control of a Kubernetes cluster. The company’s incident report, which it expanded with technical details and indicators of compromise this week, says the attacker used ARTEX, an open-source framework that runs teams of AI agents through an intrusion.

What was exposed and what customers need to do

According to Chainstack, the attacker accessed a database holding organization names, account holder names, the email addresses of organization members and password hashes. It does not store full card numbers or security codes, so those were not exposed. The attacker also had access to systems holding node credentials. Chainstack said it has no evidence those were read but is treating them as exposed.
Related articles

Illustration of rows of abstract certificate tiles turning into glowing tokens that travel along a purple-to-teal ribbon toward a cluster of linked network nodes

DTCC Tokenization Service Will Connect to Solana in the Second Half of 2027

November 12, 2026
Illustration of a glowing network of stablecoin transfer lines with a few red-flagged nodes encircled by a teal scanning ring, set against a dark grid background

Tron, Tether and Chainalysis Form Digital Crime Task Force After T3 Unit Folded

November 12, 2026

The company is emailing customers and asking them to change passwords, including anywhere the same password was reused, rotate node credentials, regenerate platform API keys if they use the platform API, and watch for phishing. Node credential rotation is self-service in the console, and current endpoints keep working until a customer rotates, so there is no downtime. “Chainstack will never ask for passwords, tokens or keys,” the report says. Customer nodes, the console and the API were not modified, according to the company, and customer-facing services ran normally throughout.

Three days from a test dashboard to production

The timeline in Chainstack’s report runs from Oct. 26, when the attacker gained access to a development environment, to Oct. 29, when they reached parts of production. Chainstack detected the intrusion on Oct. 31 and cut the access paths that day, then closed the investigation on Nov. 2. It first published the report on Nov. 3.

The entry point had been sitting there since July. A test Grafana instance in a development cluster was reachable from the internet with no single sign-on or basic authentication in front of it. Once logged in as administrator, the attacker used Grafana’s data-source proxy, which forwards requests to whatever URL a data source points at, to reach dozens of internal services. One of them was an MCP tool server, the kind of service that exposes Kubernetes operations to AI agents. It required no authentication and its service account had cluster-admin rights.

The rest followed from credentials. The attacker hijacked an automation workflow to pull a machine identity that also worked in production, read production Kubernetes secrets, then read secrets in bulk from the production cloud secrets manager. Among them was the private key of a VPN peer on the database network. Two clients presenting the same peer key made the tunnel flap and broke a database replication pipeline. That failure is what started Chainstack’s investigation. Before access was cut, the attacker had queried a production database as an administrative user and, on one PostgreSQL instance, queried the view that holds database role password hashes.

Chainstack said it found no evidence that a software vulnerability was exploited. The attack chained default credentials, exposed admin functions, missing authentication, over-broad permissions and long-lived credentials.

Why the ARTEX detail matters

Chainstack said it assesses with high confidence that ARTEX was used, citing artx and artex naming markers on resources the attacker created, use of the chisel tunneling tool, and many attack paths running in parallel with rapid retries. Google’s threat intelligence group has described ARTEX as a multi-agent penetration testing platform that several threat actors have used since late August, and CrowdStrike has tied it to a campaign against more than 200 organizations.

Chainstack was careful about what that link means. The company said it attributes the tooling, not the actor, and that none of its indicators match those published for the groups CrowdStrike and Microsoft have named.

It is the second crypto infrastructure firm in two weeks to describe an AI-assisted intrusion. Chainalysis said on Oct. 30 that an external actor used “offensive agentic techniques” against its systems, and later found credentials for all its users had been exposed, as we reported in our story on the Chainalysis breach.

Who should pay attention

The Chainstack breach matters first to its own customers. Projects that call a Chainstack endpoint with an embedded credential should rotate it, since the provider cannot rule out that those credentials were read. Teams outside Chainstack can use the report too. It lists attacker IP addresses, file hashes and Kubernetes object names, and a set of checks that would have caught the activity earlier, including Grafana proxy requests to internal addresses, unauthenticated MCP servers and the same VPN key appearing from two endpoints.

Its remediation plan, parts of which are still in progress, puts an extra authentication layer such as single sign-on in front of admin tools, strips cluster-admin rights from AI tool servers and removes any path from development to production.

FAQ

Were Chainstack customer nodes affected?
Chainstack says customer nodes, the console and the API were not modified and services ran normally. Full card numbers and security codes were not stored, so they were not exposed.

What should Chainstack users do now?
Change passwords, rotate node credentials in the console, regenerate platform API keys if used, and ignore any message asking for passwords, tokens or keys.

Was an AI model hacking Chainstack on its own?
Chainstack says the attacker used ARTEX, a framework that directs AI agents through an intrusion. It has not identified who operated it.

Disclaimer: This article is for informational purposes only and does not constitute financial advice.
Salar Salek

Salar Salek Verified AltcoinReporter Author

Salar covers cryptocurrency markets, blockchain technology, DeFi, and emerging digital asset trends for AltcoinReporter. With a background in technology and finance, he has been actively following and investing in the...

Read More
Tags: AI AgentsChainstackCybersecurityRPC Nodes

Related Posts

Illustration of rows of abstract certificate tiles turning into glowing tokens that travel along a purple-to-teal ribbon toward a cluster of linked network nodes

DTCC Tokenization Service Will Connect to Solana in the Second Half of 2027

by Salar Salek
November 12, 2026
0

DTCC plans to connect its tokenization service to Solana in the second half of 2027, adding the chain to Stellar...

Illustration of a glowing network of stablecoin transfer lines with a few red-flagged nodes encircled by a teal scanning ring, set against a dark grid background

Tron, Tether and Chainalysis Form Digital Crime Task Force After T3 Unit Folded

by Salar Salek
November 12, 2026
0

Tron, Tether and Chainalysis have launched a Digital Crime Task Force to find illicit USDT activity on Tron and feed...

Illustration of a lattice of glowing hexagonal shields closing around a central diamond-shaped crystal, with a faint clock dial behind it, on a dark purple background

Ethlabs Drops Its Own Quick Slots Push to Make Ethereum Post-Quantum by 2027

by Salar Salek
November 12, 2026
0

Ethlabs has proposed making Ethereum post-quantum in 2027 under a plan it calls pqai27, and is withdrawing its own Quick...

Illustration of a large vault of gold coins with a stream of coins flowing out toward a sealed lockbox, beside five ballot slips on a dark blue background

Zcash Vote Would Pull 50,000 ZEC From Its Grants Treasury and End the 8% Stream

by Salar Salek
November 12, 2026
0

A compromise proposal from Zooko Wilcox, Sean Bowe and Jason McGee would remove 50,000 ZEC, about $49 million, from the...

Illustration of a red crescent above a walled box of gold coins, with green tokens crossing an arched bridge to a larger glowing stack of coins on an offshore platform

FSB Urges Turkey to Set Stablecoin Rules, Cites Data Giving Binance 70% Share

by Salar Salek
November 11, 2026
0

The Financial Stability Board's peer review of Turkey calls for a dedicated stablecoin regime and tougher action on offshore platforms,...

Load More
  • Trending
  • Comments
  • Latest
Best Crypto News Apps 2026: CoinGecko vs TradingView vs CoinMarketCap

Best Crypto News Apps 2026: CoinGecko vs TradingView vs CoinMarketCap

May 6, 2026
Pi Network Completes Protocol 23 and Sets June 2 Deadline for Node Operators

Pi Network Completes Protocol 23 and Sets June 2 Deadline for Node Operators

May 27, 2026
Solana Alpenglow Upgrade 2026: Launch Date, Features, and What It Means for SOL

Solana Alpenglow Upgrade 2026: Launch Date, Features, and What It Means for SOL

April 18, 2026
Binance vs OKX in 2026: Which Global Crypto Exchange Is Actually Better?

Binance vs OKX in 2026: Which Global Crypto Exchange Is Actually Better?

June 1, 2026
North Korea’s Six-Month Con: How Hackers Stole $286M from Solana’s Drift Protocol

North Korea’s Six-Month Con: How Hackers Stole $286M from Solana’s Drift Protocol

0
Ethereum’s Glamsterdam Upgrade: What It Is and Why It Matters in 2026

Ethereum’s Glamsterdam Upgrade: What It Is and Why It Matters in 2026

0
Bitcoin’s Worst Q1 Since 2018: Can April Turn the Tide?

Bitcoin’s Worst Q1 Since 2018: Can April Turn the Tide?

0
Former UK Chancellor Kwarteng Leads Bitcoin Firm as Farage Backs BTC

Former UK Chancellor Kwarteng Leads Bitcoin Firm as Farage Backs BTC

0
Illustration of two glowing gold coins buried in layered rock strata, with light-blue lines rising from them, crossing and merging into one bright coin while two thin lines branch off to small rings, on a dark brown night background

Two 2010 Bitcoin Mining Rewards Move After 16 Years, and One Transaction Links Them

November 13, 2026
Illustration of a glowing classical bank facade with a crack in its side, a stream of small payment blocks arcing out toward a cluster of hexagonal tokens, and a padlock below the stream, on a dark blue background

Arkéa Chair Says Fake IBANs and Instant Payments Fed a €100M Heist Into Crypto

November 13, 2026
Illustration of a domed state capitol building beside a stack of gold coins with a small slice cut from the top coin, and a wooden gavel in the foreground, on a dark blue background

DOJ Backs Challenge to Illinois Digital Asset Tax as Wall Street and DeFi Groups Join

November 13, 2026
Illustration of a steel vault with a dial wheel, two gold keys and one greyed-out key around it, and a line of teal tokens leaving through a side door, on a dark teal background

Unocoin Says BitGo Freeze Held, Suspects Wallet Backup Keys Were Used to Move Funds

November 13, 2026

About

AltcoinReporter

AltcoinReporter is an independent crypto news platform built to keep you ahead of the market. We cover everything from Bitcoin and altcoins to DeFi, NFTs, regulation, and emerging blockchain technology.


Our editorial team delivers accurate news, detailed market analysis, and expert insights, with every article written and reviewed by named contributors. We are committed to transparent, independent reporting our readers can trust.

News

  • Altcoins
  • Bitcoin
  • Blockchain
  • DeFi
  • Ethereum
  • NFT

Reviews

  • Exchanges
  • NFT Marketplaces
  • Wallets

Company

  • About Us
  • Advertise
  • Write for Us
  • Contact Us

Disclaimer: AltcoinReporter.com provides cryptocurrency news for informational purposes only, not financial, investment, or legal advice. Crypto markets carry significant risk. Always do your own research and consult a financial advisor before investing. We may earn compensation through affiliate links, ads, and sponsored content, which are clearly labelled. AltcoinReporter is not responsible for any financial losses resulting from information on this site.

  • Cookie Policy
  • Ethics
  • Corrections
  • Editorial Standards
  • Privacy Policy
  • Terms & Conditions

© 2026 AltcoinReporter. All rights reserved.

No Result
View All Result
  • Home
  • News
    • Altcoins
    • Bitcoin
    • Blockchain
    • DeFi
    • Ethereum
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us

© 2026 AltcoinReporter. All rights reserved.