The U.S. Justice Department has won court authorization to seize or restrain more than $1.2 billion of the Binance hack funds taken from the exchange on Oct. 29. In the same announcement on Thursday, the department said it had taken down cloud infrastructure behind “FaceStealer,” a North Korean scheme that uses recorded webcam footage and deepfake video calls and has stolen more than $400 million over the past 18 months.
The Binance figure is the headline, but the gap around it matters more. The FBI and Binance have both blamed the theft of more than $6 billion on the North Korean group the FBI calls TraderTraitor, and most of that money is still outside anyone’s control.
What the court order covers
According to the Justice Department’s announcement, U.S. agencies and private companies have so far frozen more than $2.7 billion of the stolen assets. The department has already obtained court authorization to seize or restrain more than $1.2 billion of that amount. The release does not name the court, the companies holding the frozen funds or the specific tokens involved.
Assistant Attorney General A. Tysen Duva said the Criminal Division had used its role as the department’s liaison to the digital asset industry “to immediately halt about half of this historic breach.” M. Scott Proctor, the principal deputy head of the National Security Division, said it would use “every tool at its disposal to seize and return North Korea’s ill-gotten gains.”
A seizure or restraint order locks the assets in place while the government pursues forfeiture. It is not the same as returning funds to Binance, and the department did not say when or how any recovered assets would be distributed.
How the numbers line up with Binance’s account
Binance’s own incident report, which we covered on Nov. 3, put the loss at about $6.34 billion and said roughly $2.85 billion had been frozen or intercepted. The exchange also said it had replenished about 98% of the affected tokens with company funds.
The DOJ’s “more than $2.7 billion” frozen is close to Binance’s figure. Set against a theft of more than $6 billion, it still leaves well over $3 billion outside the freezes, and only the $1.2 billion slice is now under a U.S. court order. The department said efforts to trace and freeze the rest are continuing “as TraderTraitor actors continue to launder such assets through various cryptocurrency bridges, mixers, and exchanges.”
That laundering is still changing shape. Blockchain analytics firm Elliptic said this week that the launderers were creating worthless tokens and pushing stolen assets through decentralized exchange liquidity pools, so no funds move directly from the theft wallets to the receiving wallets, The Record reported.
FaceStealer: the video-call trap
The second half of the announcement deals with a separate campaign run out of the Central District of California. The FBI attributes FaceStealer to the North Korean cluster known as Sapphire Sleet, UNC1069, BlueNoroff and APT38, among other names.
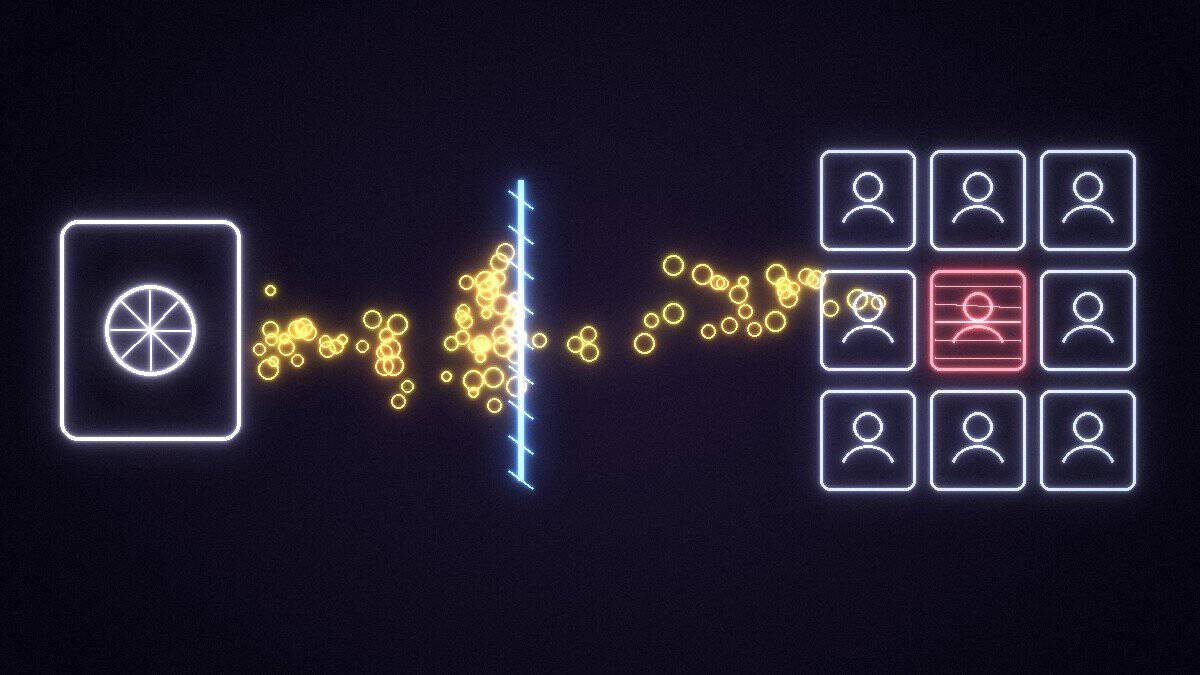
The method is simple and hard to spot. A target gets a meeting invitation from the real, hijacked account of someone they already know. Once they join, the attackers record the target’s webcam and play pre-recorded video of earlier victims, so the call appears to include familiar faces. The DOJ said the group also produces deepfake videos of well-known people in crypto and Web3. Then comes a fake technical problem, usually a claim that the target cannot be heard, and a link or prompt to “fix” it. The fix installs malware.
From there the attackers can drain wallets, take over messaging accounts and work through the new victim’s contacts. In several cases, the department said, the theft or account takeover came months or more than a year after the first compromise. Under a federal warrant the FBI seized more than 900 webcam videos of victims, and it has set up a FaceStealer resource page with a FLASH report and protection advice.
The FBI also warned that the group is now aiming the technique at open-source software developers and maintainers, seeking access to their repository accounts. That points to supply-chain attacks, where malicious code reaches users through software they already trust.
What to watch next
An FBI agent told The Record it was unclear whether FaceStealer was one of the methods used to breach Binance. Binance’s report traced its intrusion to a fake job interview. Both operations are North Korean, but the FBI names different groups: TraderTraitor for the Binance theft, and the cluster tracked as Sapphire Sleet and BlueNoroff for FaceStealer.
The next markers are a formal forfeiture filing that names the assets and court, any further freezes as the remaining funds move, and whether more of the roughly $1.5 billion frozen but not yet covered by a court order comes under one. The FBI has already published addresses tied to TraderTraitor, and the DOJ said a Cyber Alert issued last week urged crypto service providers to block transactions with or derived from the laundering addresses.
FAQ
How much of the Binance hack has the U.S. seized?
The Justice Department said it has court authorization to seize or restrain more than $1.2 billion of the Binance hack funds, out of more than $2.7 billion frozen so far by U.S. agencies and private companies.
Will the seized funds go back to Binance?
The department has not said. A seizure or restraint order holds the assets while forfeiture proceeds, and Binance has already replaced about 98% of the affected tokens from its own funds.
What is FaceStealer?
It is a North Korean social engineering scheme that uses hijacked accounts, recorded webcam video and deepfakes on fake video calls to trick targets into installing malware. The FBI says it has stolen more than $400 million in 18 months.
Disclaimer: This article is for informational purposes only and does not constitute financial advice.