• About Us
  • Advertise
AltcoinReporter
  • Home
  • News
    • Bitcoin
    • Ethereum
    • Blockchain
    • Altcoins
    • DeFi
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us
No Result
View All Result
  • Home
  • News
    • Bitcoin
    • Ethereum
    • Blockchain
    • Altcoins
    • DeFi
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us
No Result
View All Result
AltcoinReporter
No Result
View All Result
Home Exchanges

Haruko breach shows a read-only API key is not a harmless one

Salar Salek by Salar Salek
September 19, 2026
in Exchanges
Haruko breach shows a read-only API key is not a harmless one

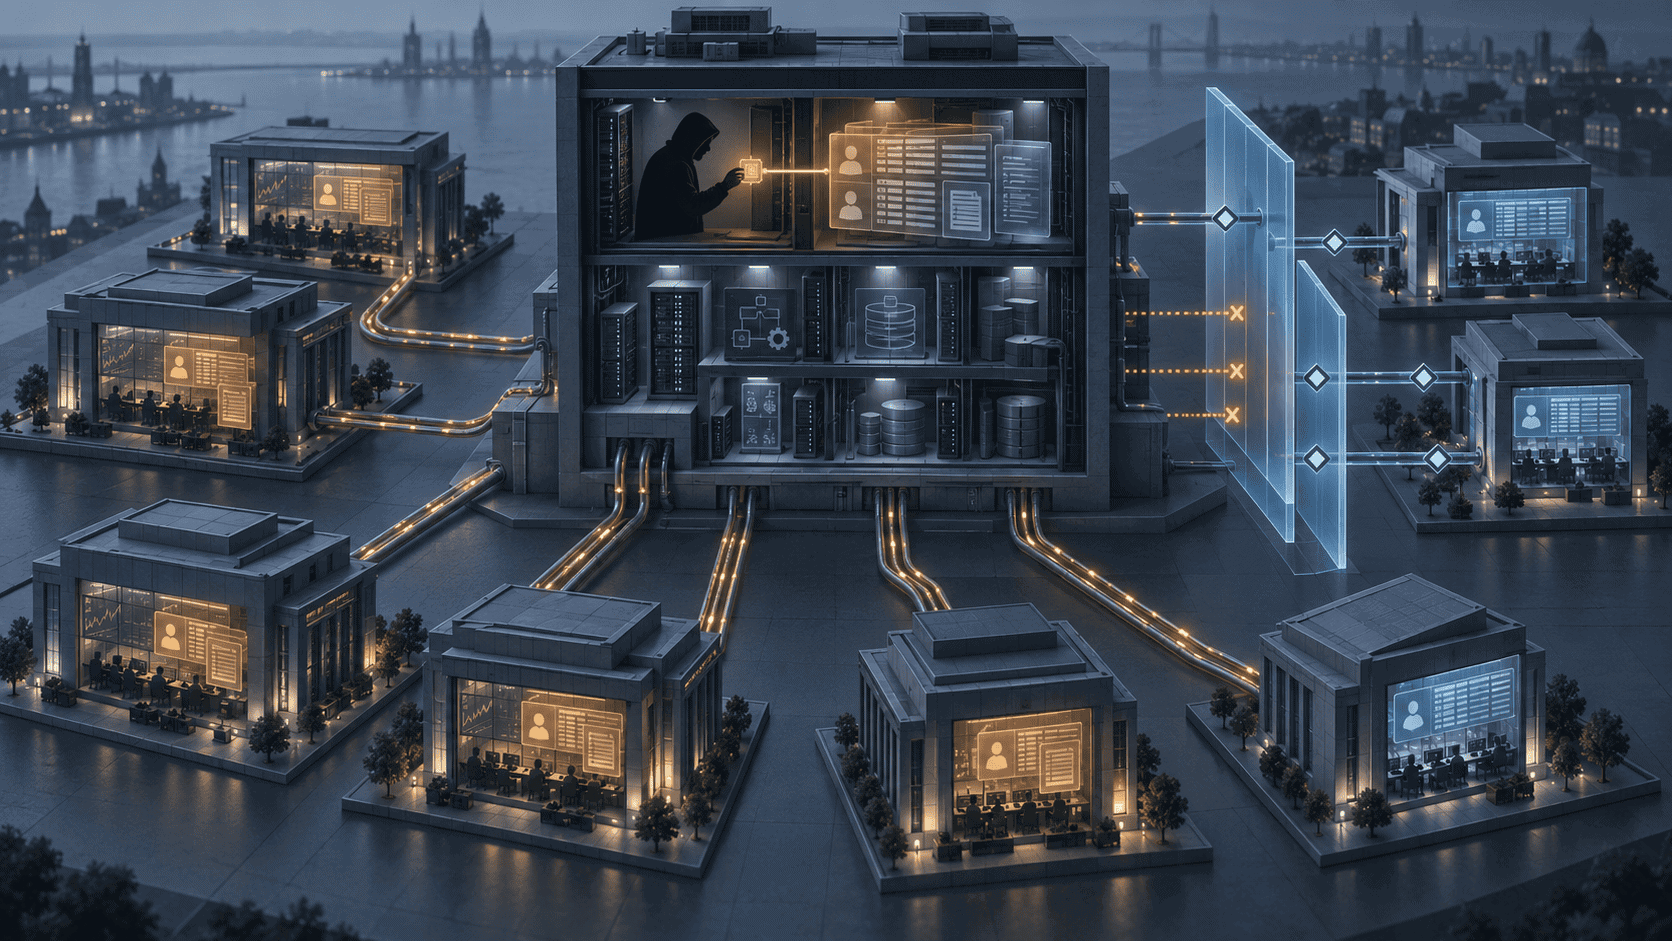
A targeted cyberattack on Haruko, a London-based technology provider serving institutional crypto firms, exposed exchange API details and trading data belonging to 15 clients, with some smaller hedge funds losing assets as a result.

The attacker exploited a vulnerability in one of Haruko’s processes, extracted a user-access token, and used it to read data held in that process’s memory, according to messages from co-founder and chief technology officer Adam Carlile reviewed by CoinDesk.
Related articles

Abstract illustration of a golden key passing between two dark geometric blocks on a deep blue background, representing a finance-chief handover

Binance CFO Kaiser Ng Confirms Exit to Build Tokenization Ventures as CZ Hints at Backing

November 8, 2026
Abstract illustration of glowing green network lines running into a dark vault wall, with three amber lines stopping short

Binance Says HYPE and APT Withdrawals Are Back, but HYPE Still Shows as Paused

November 8, 2026

That memory contained read-only exchange API details and other client data.

Carlile described it to clients as a targeted attack carried out by an organised group. The affected parties were all of Haruko’s non-whitelisted clients.

Clients’ own login credentials were not compromised on their systems.

Haruko said on 18 September that it had fixed the vulnerability and rotated server-side secrets. It did not respond to repeated requests for comment.

Read-only is not the same as harmless

The instinctive reaction to a read-only API leak is that nothing serious happened. Read-only permissions typically allow an application to see account data without placing trades or withdrawing funds.

Some clients lost money anyway.

The reason is that read-only access tells an attacker exactly what a fund holds, how it is positioned and how it trades. That is an intelligence product, not a harmless data spill.

What turns intelligence into losses is whatever else is weak at the client end. An old withdrawal permission that was never revoked. A wallet address that was never rotated. A stale API key with broader permissions than anyone remembered granting.

Smaller hedge funds with weaker security controls were particularly exposed, according to people familiar with the incident. Neither the aggregate value of the losses nor the precise method by which funds were taken has been disclosed.

That gap matters. Without knowing the mechanism, other Haruko clients cannot fully assess whether the same path exists in their own setup.

The whitelist did the work

The single most useful detail for any institution reading this is that the affected clients were all non-whitelisted.

An inbound IP whitelist restricts access to a specified list of internet addresses. Clients who had configured one were not affected. Clients who had not were.

Haruko told customers that configuring an inbound IP whitelist would provide maximum protection.

That is a configuration setting, not a product feature. It was available to every client, and 15 of them had not enabled it.

The pattern recurs across institutional crypto security. The control that would have prevented the incident usually exists and is optional, and the firms that skip it tend to be the ones with thinner operational resources.

The infrastructure choice is being questioned

Haruko runs its own bare-metal servers, physical machines it controls directly, rather than using a cloud provider such as Amazon Web Services.

That decision gives a company more control over its stack, which is a legitimate reason to make it. It also means fewer built-in layers of access monitoring and process isolation between an exploited process and whatever is sitting in its memory.

Cloud platforms bundle those guardrails by default. Bare metal requires building them.

Whether that choice caused the breach is not established, and the reporting does not confirm it. What can be said is that the attack worked by reading data out of a running process’s memory, and that isolating processes from one another is precisely the kind of protection managed platforms provide as standard.

Haruko says it serves more than 80 clients globally and connects to over 100 centralised trading venues, 30 blockchains and 250 on-chain protocols. Its client base ranges from firms such as GSR and Bitcoin Suisse down to much smaller funds.

It plans to publish a full technical post-mortem.

Infrastructure is where the money goes

The incident fits a pattern that security firms have been documenting all year, and the numbers are stark.

TRM Labs recorded 207 crypto attacks in the first half of 2026, more than double the 83 logged a year earlier, resulting in roughly $972 million in losses.

The distribution is the important part. Infrastructure and operational compromises accounted for about 76% of the money stolen while representing only 15% of incidents.

CertiK, using a different methodology, put first-half losses at approximately $1.32 billion across 344 incidents. The two figures are not directly comparable, but both point the same way.

Attacking a smart contract requires finding a flaw in code that has usually been audited. Attacking the service provider that dozens of firms depend on reaches all of them at once, and the failure is operational rather than cryptographic.

Haruko sits in exactly that position. A single vulnerability in one process reached 15 institutional clients simultaneously.

What clients should check

The practical response is narrow and does not require waiting for the post-mortem.

Enable inbound IP whitelisting where a provider offers it. Audit every API key currently issued and confirm what permissions each actually carries rather than what it was meant to carry. Revoke anything unused. Rotate withdrawal addresses that have been static for long periods.

The broader question is harder. Institutional crypto now runs on a small number of technology providers that sit between funds and exchanges, and those providers concentrate risk by design. A fund can have excellent internal controls and still be exposed through a vendor it does not operate.

That is not unique to crypto. What is unique is that the transactions are irreversible, which removes the recovery mechanism most of traditional finance relies on when operational security fails.

FAQ

What was exposed?
Read-only exchange API details and trading data for 15 institutional clients. Attackers exploited a vulnerability in one of Haruko’s processes, extracted an access token, and read data from that process’s memory. Client login credentials on their own systems were not compromised.

How did funds get stolen from a read-only leak?
Read-only access reveals what a fund holds and how it trades. Combined with weaknesses at the client end, such as an unrevoked withdrawal permission or an unrotated wallet address, that information can be converted into losses. The precise method and amounts have not been disclosed.

Who was affected?
All 15 affected clients were non-whitelisted, meaning they had not configured an inbound IP whitelist restricting access to approved addresses. Haruko has told clients that enabling one provides maximum protection.

Disclaimer: This article is for informational purposes only and does not constitute financial or security advice. Cryptocurrency investments carry significant risk. Always conduct your own research before making any investment decisions.
Salar Salek

Salar Salek Verified AltcoinReporter Author

Salar covers cryptocurrency markets, blockchain technology, DeFi, and emerging digital asset trends for AltcoinReporter. With a background in technology and finance, he has been actively following and investing in the...

Read More
Tags: API securitycyberattackHarukohedge fundsinstitutional crypto

Related Posts

Abstract illustration of a golden key passing between two dark geometric blocks on a deep blue background, representing a finance-chief handover

Binance CFO Kaiser Ng Confirms Exit to Build Tokenization Ventures as CZ Hints at Backing

by Salar Salek
November 8, 2026
0

Outgoing Binance CFO Kaiser Ng said on Sunday he will build tokenization projects in sports, music, GPUs, robotics, gold and...

Abstract illustration of glowing green network lines running into a dark vault wall, with three amber lines stopping short

Binance Says HYPE and APT Withdrawals Are Back, but HYPE Still Shows as Paused

by Salar Salek
November 8, 2026
0

Binance added HYPE and APT to its restored-withdrawals list on Sunday. Its own network status data still showed HYPE paused...

Abstract exchange booths converting coins into digital particles behind translucent financial barriers

OFAC Sanctions Eight Canadian Money Services Firms Over Iran Crypto Links

by Salar Salek
November 8, 2026
0

OFAC designated eight Canada-based money services businesses under Executive Order 13902. Overlapping aliases and six listed Tron addresses make entity-level...

Neon illustration of three coins behind a gate on a pedestal next to a calendar grid with one highlighted day

Bank of Russia Clears Bitcoin, Ether and USDT for Retail Buyers From Nov. 17

by Salar Salek
November 7, 2026
0

The Bank of Russia approved Bitcoin, Ether and USDT as the only cryptocurrencies non-qualified investors can buy, with a 300,000-ruble...

Neon illustration of a trading screen and coin stack sending streams of tokens across a dashed border to offshore server racks

India’s ED Alleges CoinDCX Routed Users’ Trades Offshore Through a Costa Rica Account

by Salar Salek
November 7, 2026
0

The Enforcement Directorate searched premises linked to CoinDCX and Delta Exchange India under FEMA and alleges user trades were executed...

Load More
  • Trending
  • Comments
  • Latest
Pi Network Completes Protocol 23 and Sets June 2 Deadline for Node Operators

Pi Network Completes Protocol 23 and Sets June 2 Deadline for Node Operators

May 27, 2026
Best Crypto News Apps 2026: CoinGecko vs TradingView vs CoinMarketCap

Best Crypto News Apps 2026: CoinGecko vs TradingView vs CoinMarketCap

May 6, 2026
Solana Alpenglow Upgrade 2026: Launch Date, Features, and What It Means for SOL

Solana Alpenglow Upgrade 2026: Launch Date, Features, and What It Means for SOL

April 18, 2026
Binance vs OKX in 2026: Which Global Crypto Exchange Is Actually Better?

Binance vs OKX in 2026: Which Global Crypto Exchange Is Actually Better?

June 1, 2026
North Korea’s Six-Month Con: How Hackers Stole $286M from Solana’s Drift Protocol

North Korea’s Six-Month Con: How Hackers Stole $286M from Solana’s Drift Protocol

0
Ethereum’s Glamsterdam Upgrade: What It Is and Why It Matters in 2026

Ethereum’s Glamsterdam Upgrade: What It Is and Why It Matters in 2026

0
Bitcoin’s Worst Q1 Since 2018: Can April Turn the Tide?

Bitcoin’s Worst Q1 Since 2018: Can April Turn the Tide?

0
Former UK Chancellor Kwarteng Leads Bitcoin Firm as Farage Backs BTC

Former UK Chancellor Kwarteng Leads Bitcoin Firm as Farage Backs BTC

0
Illustration of a row of server racks with their lights powered down and one rack glowing amber in a dark server corridor

LNbits Disables All Hosted Instances After Attacks, Tells Users to Stop Servers

November 8, 2026
Abstract illustration of a golden key passing between two dark geometric blocks on a deep blue background, representing a finance-chief handover

Binance CFO Kaiser Ng Confirms Exit to Build Tokenization Ventures as CZ Hints at Backing

November 8, 2026
Illustration of a glowing blue faceted crystal on a dark background with faint orange specks, representing ETH as a store of value and a shrinking fee burn

Vitalik Wants ETH Judged as a Store of Value as Burn Covers 3% of Issuance

November 8, 2026
Abstract illustration of glowing green network lines running into a dark vault wall, with three amber lines stopping short

Binance Says HYPE and APT Withdrawals Are Back, but HYPE Still Shows as Paused

November 8, 2026

About

AltcoinReporter

AltcoinReporter is an independent crypto news platform built to keep you ahead of the market. We cover everything from Bitcoin and altcoins to DeFi, NFTs, regulation, and emerging blockchain technology.


Our editorial team delivers accurate news, detailed market analysis, and expert insights, with every article written and reviewed by named contributors. We are committed to transparent, independent reporting our readers can trust.

News

  • Altcoins
  • Bitcoin
  • Blockchain
  • DeFi
  • Ethereum
  • NFT

Reviews

  • Exchanges
  • NFT Marketplaces
  • Wallets

Company

  • About Us
  • Advertise
  • Write for Us
  • Contact Us

Disclaimer: AltcoinReporter.com provides cryptocurrency news for informational purposes only, not financial, investment, or legal advice. Crypto markets carry significant risk. Always do your own research and consult a financial advisor before investing. We may earn compensation through affiliate links, ads, and sponsored content, which are clearly labelled. AltcoinReporter is not responsible for any financial losses resulting from information on this site.

  • Cookie Policy
  • Ethics
  • Corrections
  • Editorial Standards
  • Privacy Policy
  • Terms & Conditions

© 2026 AltcoinReporter. All rights reserved.

No Result
View All Result
  • Home
  • News
    • Altcoins
    • Bitcoin
    • Blockchain
    • DeFi
    • Ethereum
    • NFT
  • Press Releases
  • Reviews
    • Exchanges
    • NFT Marketplaces
    • Wallets
  • Market Analysis
  • Contact Us

© 2026 AltcoinReporter. All rights reserved.